Introduction
Aaj ke digital world me online security pehle se zyada important ho gayi hai. Log banking, shopping, social media, healthcare, and business services ke liye internet ka use karte hain. Jitni zyada online activity increase hui hai, utna hi unauthorized access aur account theft ka risk bhi barha hai.
Traditional passwords security ka basic method hain, lekin sirf password par depend karna hamesha safe nahi hota. Weak passwords, password reuse, phishing attacks, aur data breaches ki wajah se users ke accounts compromise ho sakte hain.
Isi problem ko solve karne ke liye One Time Password (OTP) authentication ka use kiya jata hai.
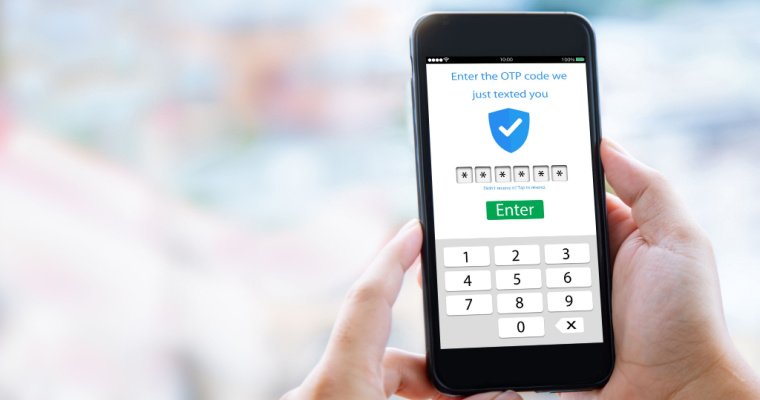
A One Time Password ek temporary security code hota hai jo sirf ek baar use kiya ja sakta hai aur limited time ke liye valid hota hai. OTP ka purpose ye ensure karna hota hai ke account access karne wala user asal owner hi hai.
Aaj OTP banking, online payments, mobile applications, social media accounts, business systems, aur many digital services me security layer ke taur par use hota hai.
What Is a One Time Password (OTP)?
One Time Password (OTP) ek automatically generated security code hota hai jo user ki identity verify karne ke liye use hota hai.
Normal password ke unlike, OTP:
- Sirf ek baar use hota hai
- Limited time ke baad expire ho jata hai
- Har login ya transaction ke liye naya generate hota hai
Usually OTP 4, 6, ya 8 digits ka numeric code hota hai, lekin kuch systems me letters aur numbers ka combination bhi use kiya ja sakta hai.
Example:
A user apne bank account me login karta hai.
- User username aur password enter karta hai.
- Bank ek OTP generate karta hai.
- OTP registered mobile number ya authentication app par send hota hai.
- User code enter karta hai.
- System verify karta hai aur access allow karta hai.
Agar OTP correct hai aur valid time ke andar enter kiya gaya hai, to user successfully authenticate ho jata hai.
Why Was One Time Password Created?
Traditional passwords ke sath kai security problems hain.
Weak Passwords
Many users simple passwords use karte hain jo hackers easily guess kar sakte hain.
Examples:
- Password123
- Birthday dates
- Common words
Password Reuse
Users aksar same password multiple websites par use karte hain.
Agar ek website ka password leak ho jaye, to attacker doosre accounts tak bhi access kar sakta hai.
Data Breaches
Large companies ke data breaches me millions of usernames aur passwords expose ho sakte hain.
OTP additional protection provide karta hai kyun ke stolen password ke sath bhi attacker ko temporary code ki zaroorat hoti hai.
How Does a One Time Password Work?
OTP authentication ek secure process follow karta hai.
Step 1: User Requests Access
User kisi account me login ya transaction start karta hai.
Example:
- Banking app login
- Online payment
- Account verification
Step 2: System User Information Verify Karta Hai
System check karta hai:
- Username
- Password
- Registered phone number
- Email address
Step 3: OTP Generate Hota Hai
Authentication system ek unique temporary code generate karta hai.
Ye code random hota hai aur previous OTP se different hota hai.
Step 4: OTP User Ko Send Kiya Jata Hai
OTP different methods se deliver ho sakta hai:
- SMS
- Authentication app
- Push notification
- Hardware token
Step 5: User OTP Enter Karta Hai
User received code enter karta hai.
System verify karta hai:
- Code correct hai ya nahi
- Code expire to nahi hua
- Code pehle use to nahi hua
Step 6: Access Granted
Agar information match ho jaye to system user ko access provide kar deta hai.
Types of One Time Passwords
Different organizations apni security requirements ke according different OTP methods use karti hain.
1. SMS One Time Password
SMS OTP sabse common OTP method hai.
Isme security code user ke registered mobile number par text message ke through send hota hai.
Example:
“Your verification code is 483921”
Where SMS OTP Is Used:
- Banking apps
- Mobile wallets
- Social media accounts
- E-commerce websites
Advantages:
- Easy to use
- Extra application ki zaroorat nahi
- Almost every mobile user access kar sakta hai
Limitations:
- Network delays
- SIM swap attacks
- Mobile signal dependency
2. Email OTP
Email OTP me verification code user ke registered email address par send hota hai.
Common uses:
- New account verification
- Password recovery
- Login confirmation
Advantages:
- Easy access
- Useful when phone number unavailable
Limitations:
- Email account compromise hone ka risk
3. Time-Based One Time Password (TOTP)
TOTP advanced OTP method hai jo authentication apps ke through generate hota hai.
Examples:
- Google Authenticator
- Microsoft Authenticator
- Authy
Is system me code automatically har kuch seconds ke baad change hota rehta hai.
Benefits:
- SMS se zyada secure
- Internet connection ki zaroorat nahi hoti
- Phishing risk kam hota hai
4. Push Notification Authentication
Is method me user ko mobile app notification receive hoti hai.
Example:
“Are you trying to log in?”
User approve ya reject karta hai.
Ye method banking aur business applications me popular hai.
5. Hardware Token OTP
Hardware tokens physical devices hote hain jo OTP generate karte hain.
Ye mostly use hote hain:
- Large organizations
- Government systems
- High-security environments
Difference Between OTP and Password
| Feature | One Time Password | Traditional Password |
|---|---|---|
| Usage | One time | Multiple times |
| Validity | Short period | Long term |
| Security | Higher | Depends on strength |
| Memory | User ko yaad nahi rakhna | User remembers |
| Generation | Automatically created | User creates |
OTP password ka replacement nahi hota, balki aksar password ke sath extra security layer ke taur par use hota hai.
Benefits of One Time Password
1. Better Account Security
OTP unauthorized users ko access karne se rokne me help karta hai.
Agar kisi ke paas password aa bhi jaye, OTP ke baghair login mushkil hota hai.
2. Two-Factor Authentication Support
OTP commonly 2FA (Two-Factor Authentication) ka part hota hai.
2FA me user ko do verification methods complete karne hote hain:
- Something you know (password)
- Something you have (phone/device)
3. Protection Against Password Theft
OTP temporary hota hai, isliye stolen code generally dobara use nahi kiya ja sakta.
4. User Convenience
Users ko complicated security processes yaad nahi rakhne padte.
Common OTP Security Risks
Although OTP security improve karta hai, kuch risks exist karte hain.
Phishing Attacks
Attackers fake messages ya websites create karke users se OTP demand kar sakte hain.
Example:
“Your account will be blocked. Share OTP immediately.”
Real companies kabhi OTP share karne ko nahi kehti.
SIM Swap Attacks
SIM swap me attacker victim ka phone number apne SIM par transfer karwa leta hai.
Isse SMS OTP receive kiya ja sakta hai.
Malware Attacks
Malicious applications OTP messages read karne ki koshish kar sakti hain.
How To Keep Your OTP Safe?
Follow these security practices:
Never Share Your OTP
OTP sirf aapke personal verification ke liye hota hai.
Kisi person, call, ya message par share na karein.
Avoid Suspicious Links
Unknown links par login details ya OTP enter na karein.
Use Authentication Apps
Important accounts ke liye SMS ke bajaye TOTP apps zyada secure option ho sakti hain.
Enable Security Alerts
Login notifications aur account alerts activate rakhein.
Uses of One Time Password in Different Industries
Banking Sector
Banks OTP use karte hain:
- Login verification
- Money transfers
- New device approval
E-commerce
Online stores use karte hain:
- Account creation
- Payment verification
- Order security
Healthcare
Healthcare platforms OTP use karte hain:
- Patient verification
- Secure access
Business Systems
Companies OTP use karti hain:
- Employee login
- Remote access security
- Data protection
Future of One Time Password Authentication
Technology evolve ho rahi hai aur authentication methods bhi improve ho rahe hain.
Future me OTP ke sath ye technologies important hongi:
- Biometric authentication
- Passwordless login
- Security keys
- AI-based fraud detection
Although new technologies develop ho rahi hain, OTP abhi bhi online security ka important part hai.
Frequently Asked Questions About One Time Password
What is a One Time Password?
A One Time Password is a temporary security code used to verify a user’s identity during login, transactions, or account verification.
How long does an OTP remain valid?
Most OTP codes remain valid for a few minutes, depending on the service provider.
Is OTP completely secure?
OTP improves security but users must still protect themselves from phishing, scams, and unauthorized requests.
Can someone use my OTP?
A valid OTP can be used by someone else if they obtain it before expiration, which is why OTP should never be shared.
What is the difference between OTP and 2FA?
OTP is a verification code, while 2FA is a security method that uses two different authentication factors. OTP is commonly used as one part of 2FA.
Conclusion
A One Time Password (OTP) is one of the most widely used security methods for protecting online accounts and digital transactions. By providing a temporary verification code, OTP adds an extra layer of protection beyond traditional passwords.
From banking and shopping to business systems and social media, OTP authentication helps confirm user identity and reduce unauthorized access risks.
However, users must remain careful because security depends not only on technology but also on safe online habits. Never sharing OTP codes, avoiding suspicious messages, and using trusted authentication methods can help maintain stronger digital security.
As online threats continue to evolve, One Time Password technology will remain an important tool in creating safer digital experiences.